
Cyber Citadel has launched Citadel53, a security management platform that gives organisations a single, consolidated view of their Microsoft cloud security posture, identity risk, compliance standing, and Azure spend. Citadel53 is available now through the Azure Marketplace.
Most organisations running Microsoft 365 and Azure are already paying for good telemetry: their security data is already automatically collected for monitoring and analysis. The difficulty is that it lives in seven or more separate consoles.
Defender reports on endpoints, Entra ID on identity, Intune on device compliance, Secure Score on configuration, and Cost Management on spend, each with its own login, its own export format, and its own view of what matters. Assembling those into a coherent picture is laborious and time-consuming work, at best accomplished once a month with a good IT team.
One thing is clear: security teams do not need another place to send their data. They just need that data to answer their questions. And that is where Citadel53 comes in.
Citadel53 reads everything from Microsoft data sources and renders them as one prioritised view. Alerts are ranked across consoles, vulnerabilities sorted by exploitability, identity gaps such as unused licences flagged, cost anomalies highlighted, and security posture trends revealed.
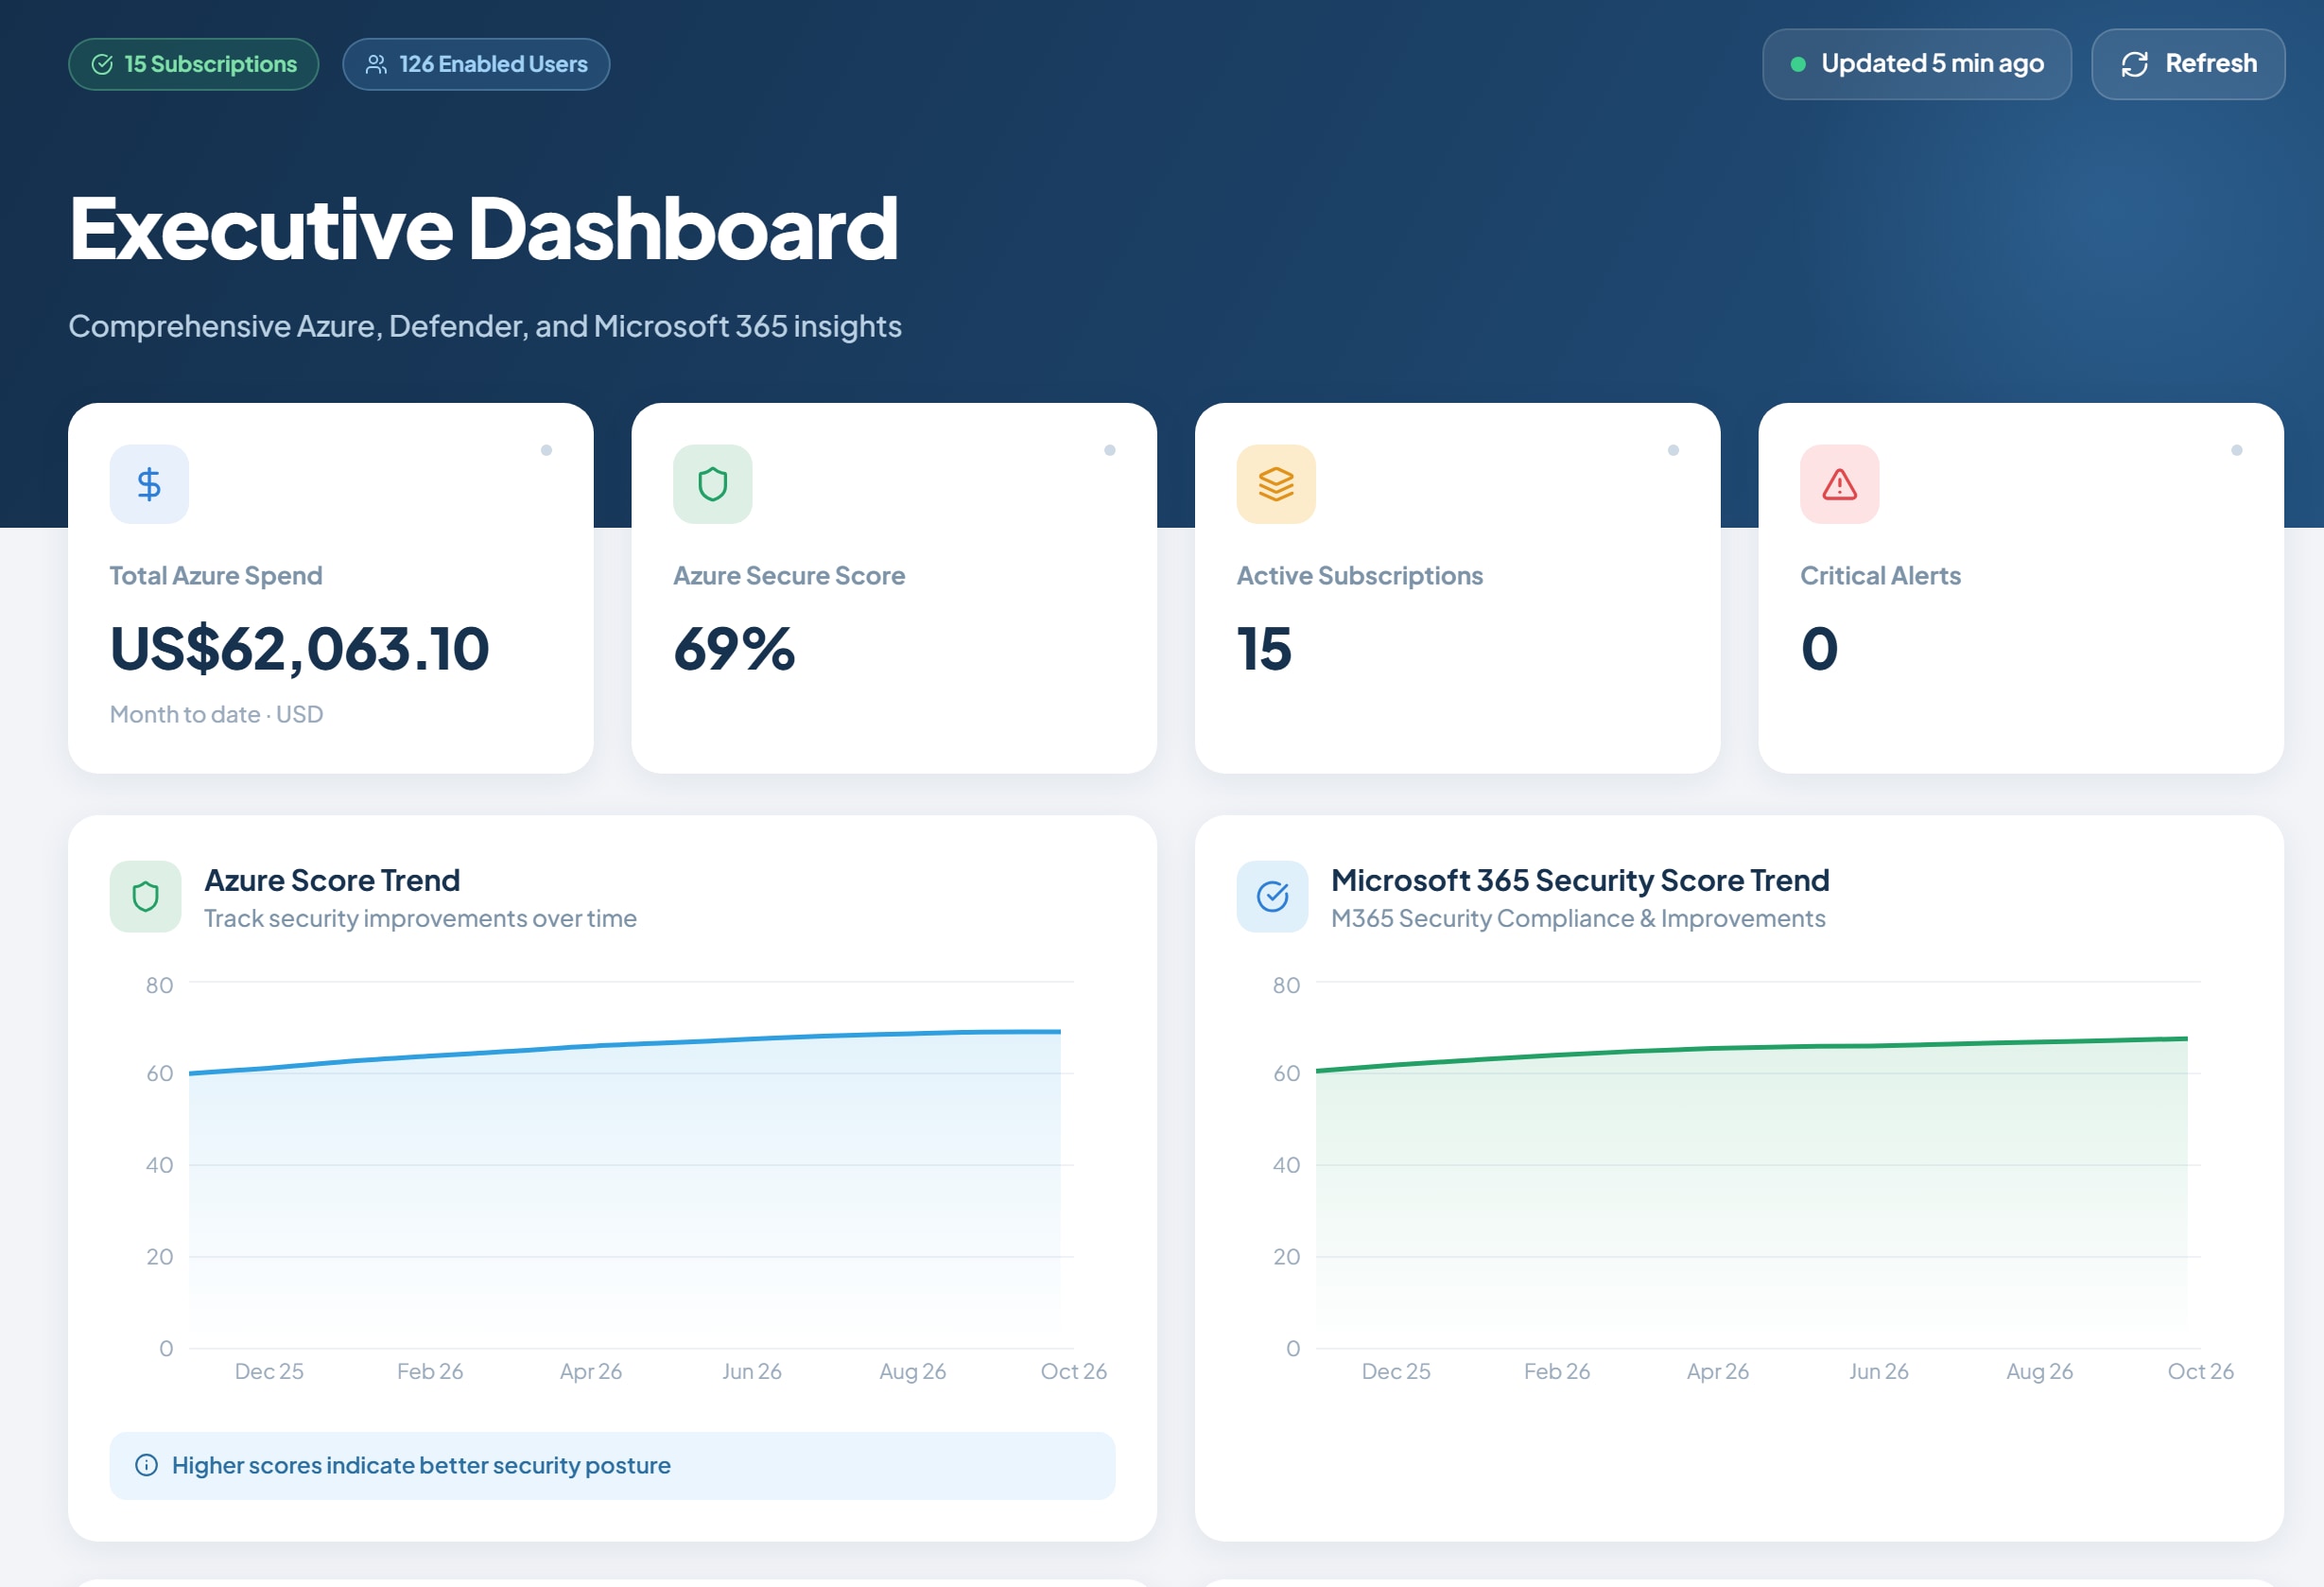
Your data stays in your tenant
Citadel53 is not a SaaS platform that customers upload their data to. It is a Managed Application, deployed from the Azure Marketplace into the customer's own tenant in around fifteen minutes. Connections are read-only, there are no agents to install on endpoints, and data never leaves the tenant.
Citadel53 simply reads Microsoft data sources, telling you what you really need to know.
Built for managed service providers
For MSSPs, the console problem is multiplied by the client count. But not with Citadel53.
A single Citadel53 login manages an unlimited number of client tenants, with a risk-sorted client directory, full data segregation between them, and drill-down without re-authenticating. Reporting is white labelled throughout: providers set their own logos, colours, and report headers, and end clients never see third-party branding. Cyber Citadel estimates that running eight or more tenants through Citadel53 recovers more than 150 hours work a month, currently spent assembling client reports by hand.
Citadel53 is handing back analyst time, which is better spent on critical security work than on mindless clerical tasks.
Compliance evidence generated
Citadel53 scores an organisation against the ASD Essential Eight automatically, mapping each control to the Microsoft signal that evidences it. Evidence panels, attestation forms, and audit-ready exports are produced in seconds.
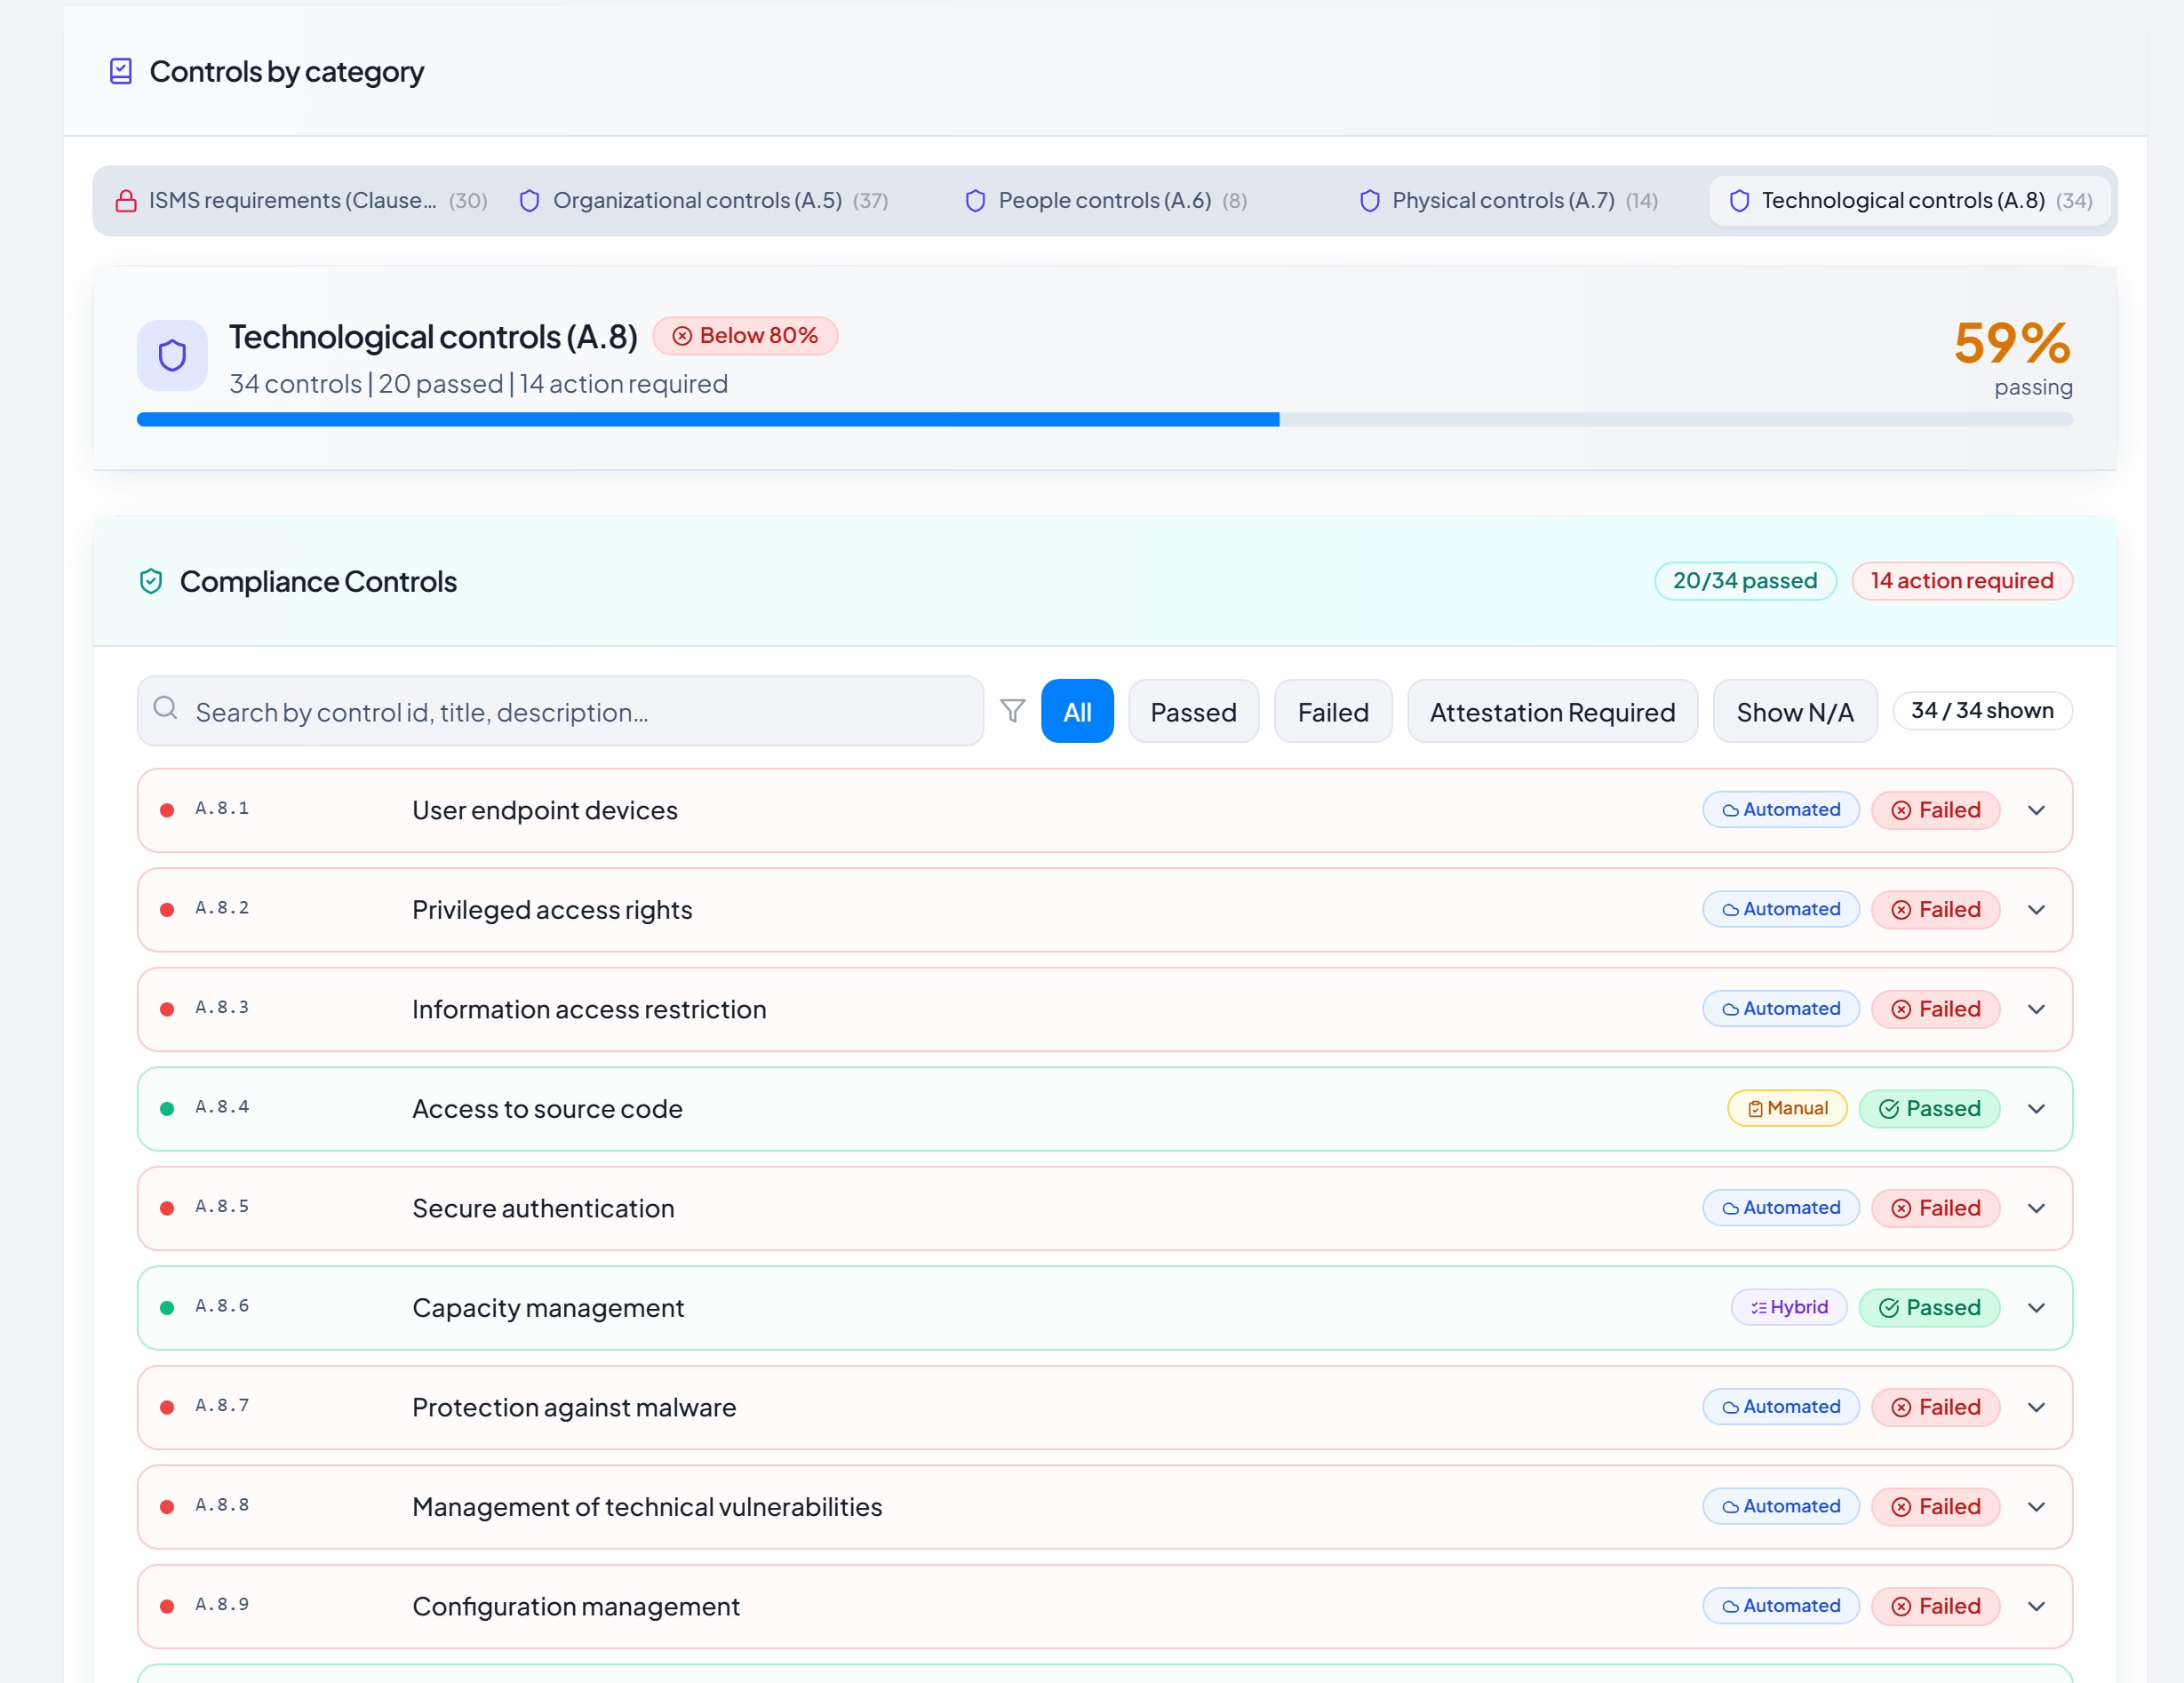
Those controls overlap substantially with the Information Security Manual, ISO 27001, and SOC 2, which means the same evidence base supports wider assurance and compliance work. That matters more than usual this year: in June 2026 the ASD confirmed that the Essential Eight will be retired within two years and replaced by its new Essentials series. The framework document might be changing. The underlying controls, and the data that evidence them, are not. This means that organisations building that evidence now will not be building it twice.
AI that supports you
Citadel53 AI follows the same principles. It runs on your own Azure OpenAI service, reads your data with read-only access, and never changes anything in Microsoft 365 or Azure. The CVE Analyst checks the past week's CVEs against the software on your devices and the services in your Azure, shows which ones affect you and which devices are exposed, ranks what to fix now, and says plainly what it could not check. The AI chat answers questions about any CVE in plain English from your Defender, Intune and Azure data, every scan and chat can be saved as a branded PDF report, and policy drafting writes a first draft of any security policy for a person to approve.
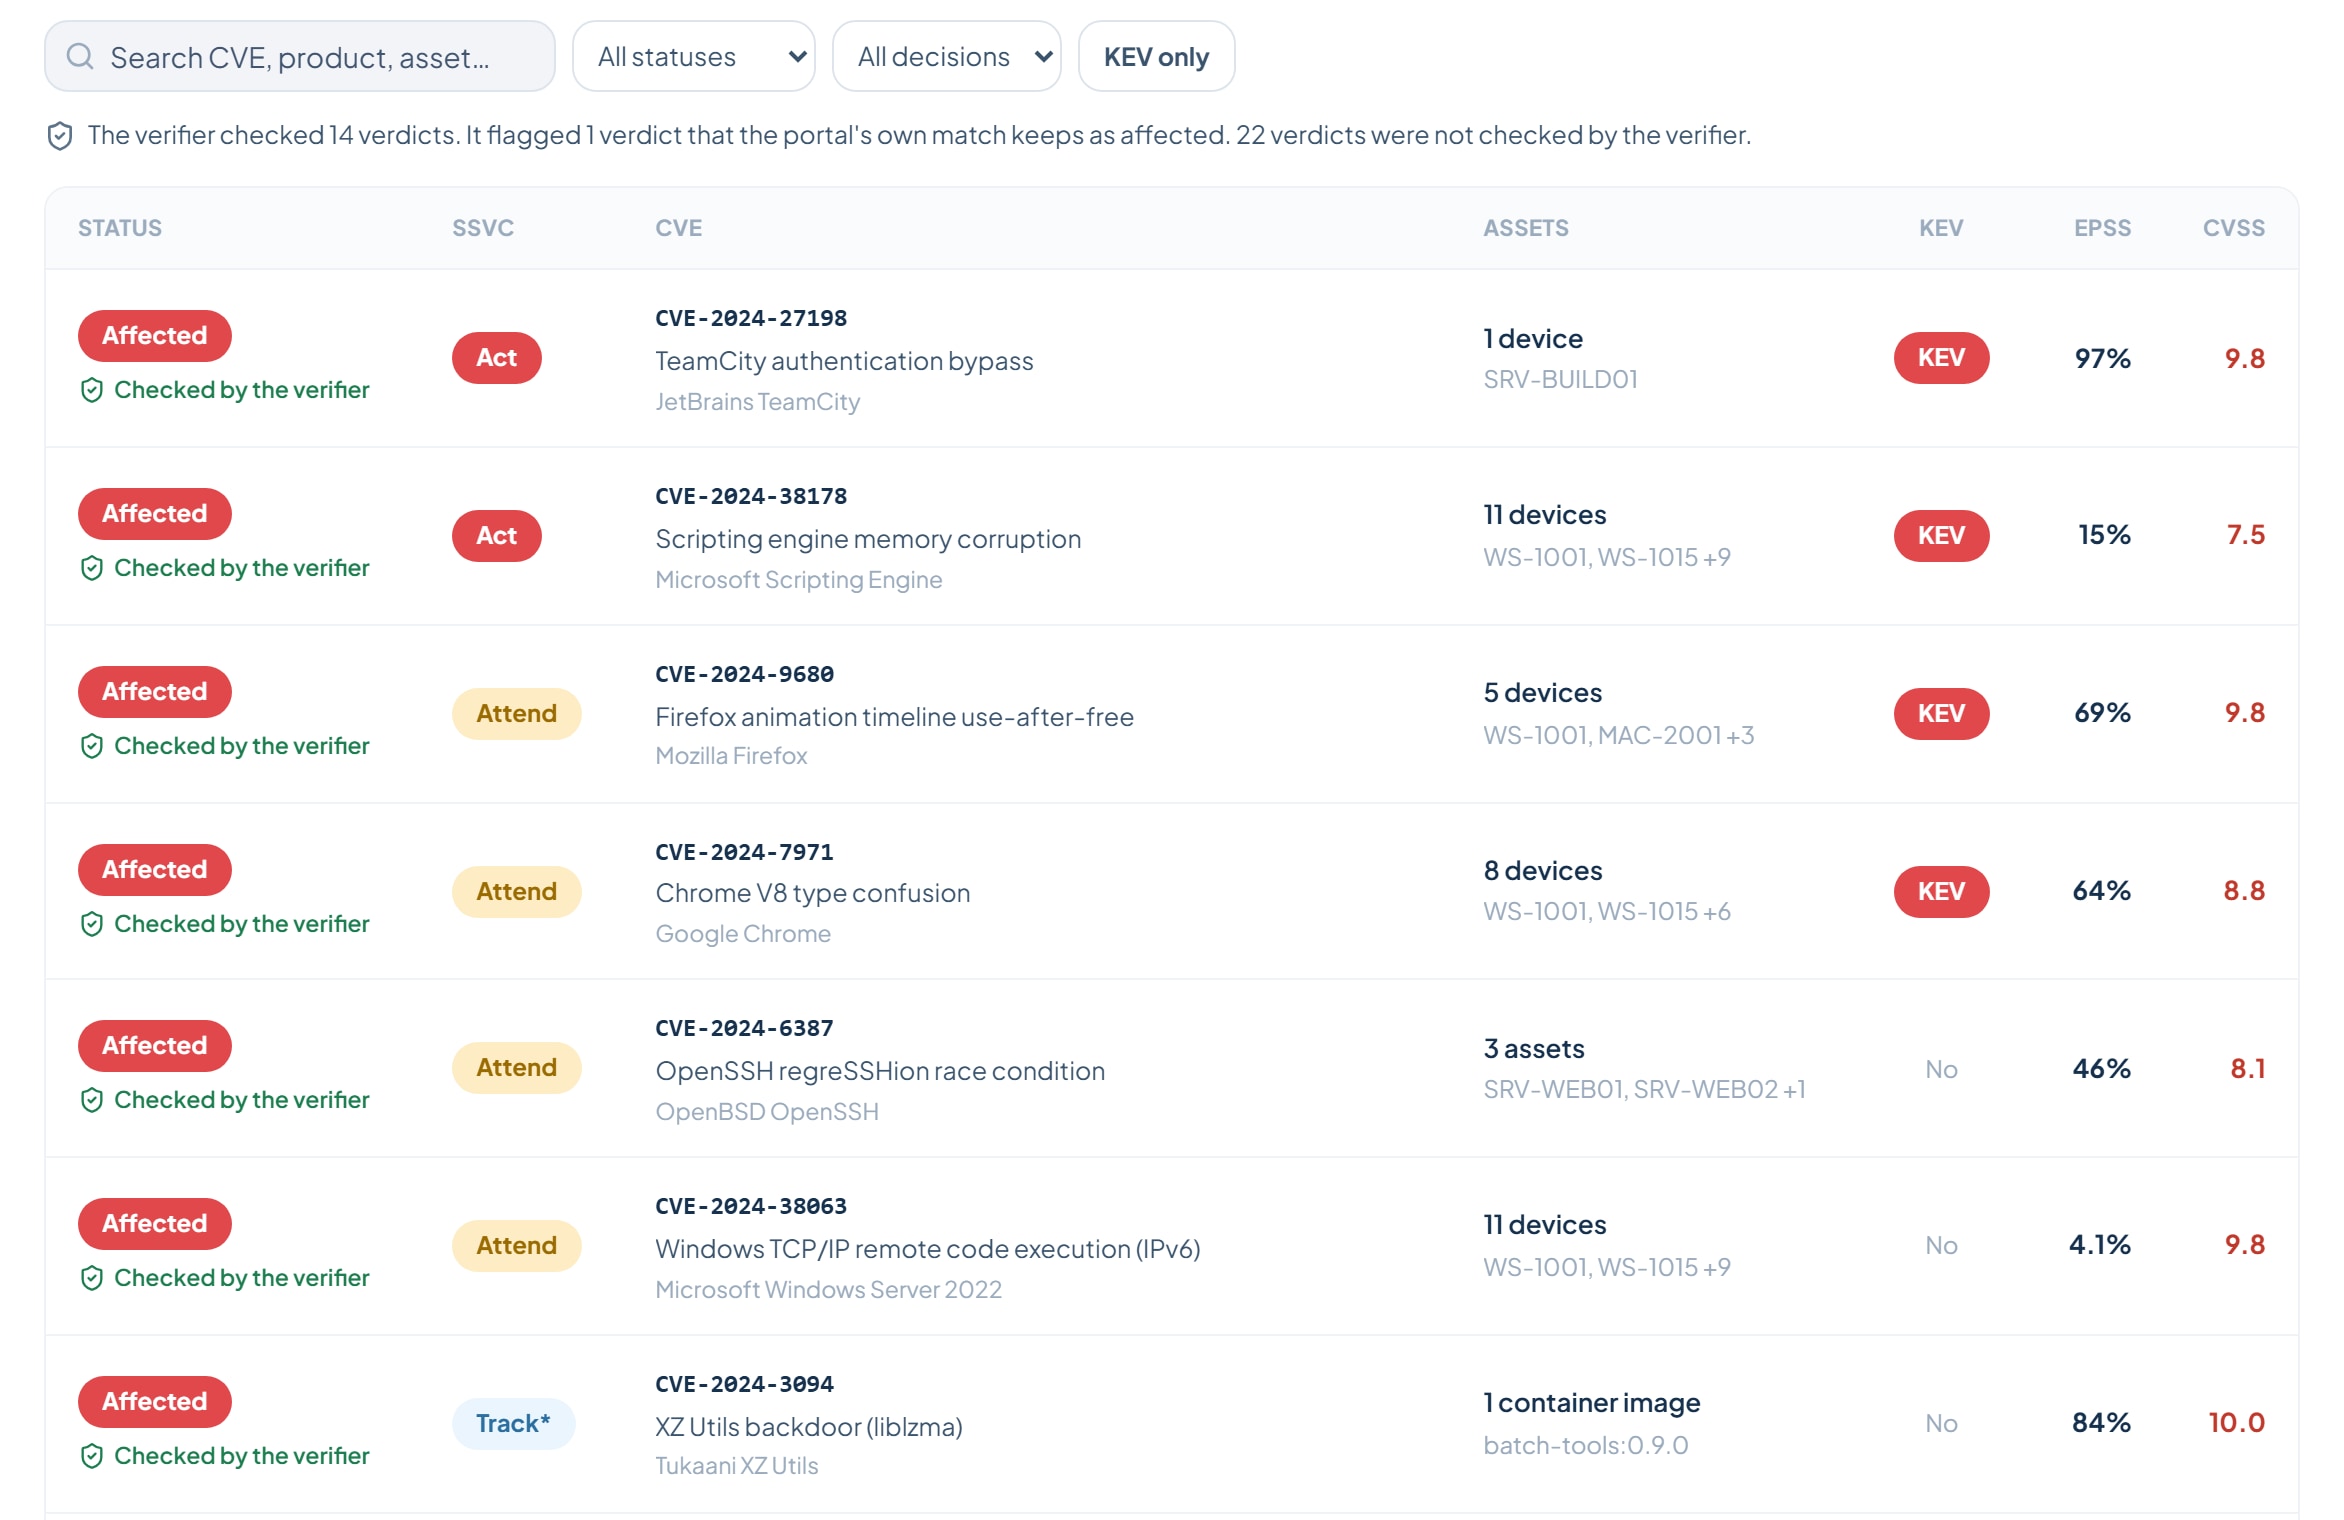
Citadel53 AI is designed for you, not for Cyber Citadel. It is not a chat bot working from a script, but a tool that knows your environment and shows the evidence behind every answer.
Availability
Citadel53 is available now on the Azure Marketplace in three tiers: a perpetually Free Tier covering one organisation and up to two Azure subscriptions; a paid Standalone Tier, for single organisations needing full reporting and compliance auditing; and a paid Multi-MSSP Portal Tier, for providers managing multiple client tenants. Both paid tiers include a commitment-free fourteen-day trial, which includes a demonstration environment with realistic seed data.
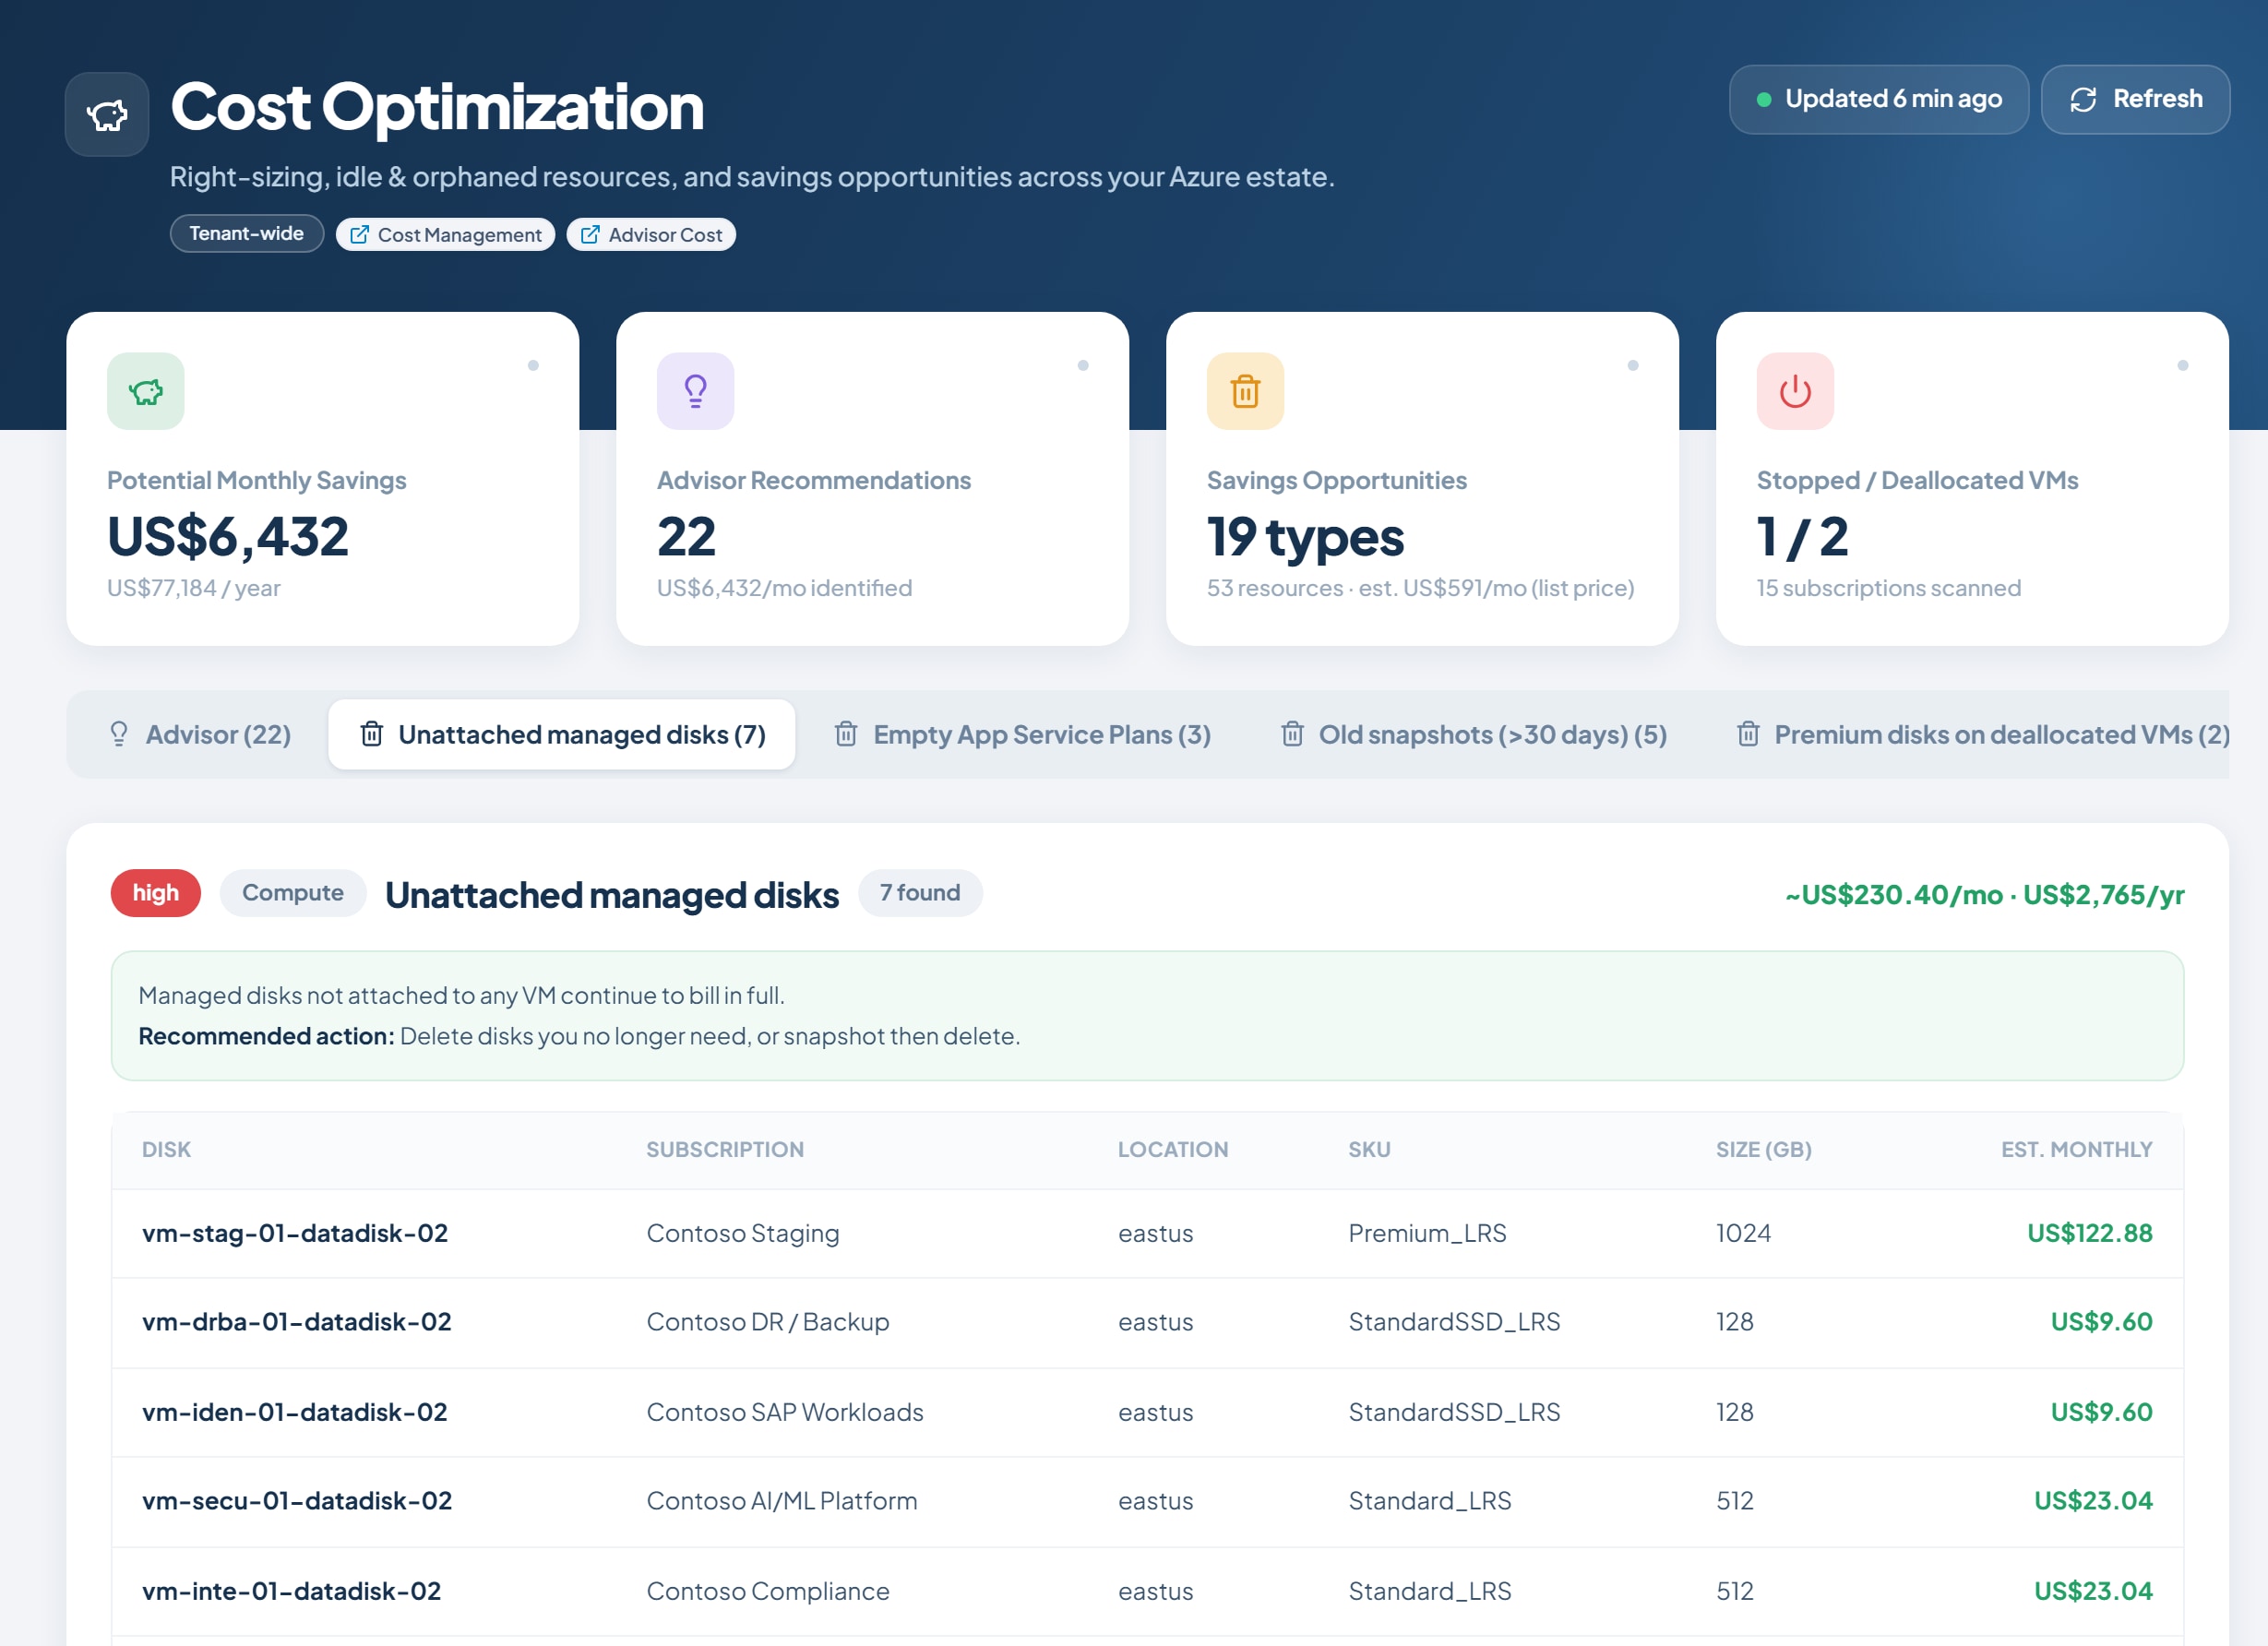
See it for yourself
Book a free 30-minute consultation to see Citadel53 on sample data and get answers about your own Microsoft 365 and Azure, or get Citadel53 on the Azure Marketplace.
Read more about Citadel53 on its page on this site and at citadel53.com, where this release is also published: Cyber Citadel launches Citadel53.